
Free Preparation Discussions
 MENU

IAPP CIPT Exam Questions
- Topic 1: Privacy Risks, Threats and Violations: This section of the CIPT exam assesses the ability of information privacy technologists to connect data ethics and data privacy. It also evaluates your proficiency in minimizing privacy risks during personal data collection, use, and dissemination, including mitigating intrusion and decisional interference threats. Finally, your knowledge of software security-related privacy risks will be tested.
- Topic 2: Privacy-Enhancing Strategies, Techniques and Technologies: Information privacy technologists will have their skills evaluated on identifying and implementing data-oriented, process-oriented, and data protection strategies, including privacy-enhancing techniques, in this portion of the CIPT exam.
- Topic 3: Privacy Engineering: This topic tests the understanding of information privacy technologists about privacy engineering organizational role and objectives. Your ability to identify and evaluate privacy design patterns and manage privacy risks throughout the development lifecycle will be measured.
- Topic 4: Evolving or Emerging Technologies in Privacy: In this section, the CIPT exam gauges the comprehension of information privacy technologist about privacy implications related to robotics and IoT, e-commerce, biometrics, and technology use in the workplace.
- Topic 5: Privacy by Design: This section will measure skills of information privacy technologist in implementing the privacy by design methodology, evaluating privacy risks in user experiences, applying Value Sensitive Design, and managing privacy-related functions and controls.
- Topic 6: The Privacy Technologist’s Role in the Context of the Organization: Here, the CIPT exam assesses the grasp of information privacy technologists of general, technical, and specialized roles and responsibilities within an organization.
- Topic 7: Foundational Principles: This section of the CIPT exam will test the knowledge of information privacy technologists about privacy risk models and frameworks, privacy by design principles, privacy-related technology fundamentals, and the data life cycle.
Free IAPP CIPT Exam Actual Questions
Note: Premium Questions for CIPT were last updated On Nov. 09, 2026 (see below)
SCENARIO
Clean-Q is a company that offers house-hold and office cleaning services. The company receives requests from consumers via their website and telephone, to book cleaning services. Based on the type and size of service, Clean-Q then contracts individuals that are registered on its resource database - currently managed in-house by Clean-Q IT Support. Because of Clean-Q's business model, resources are contracted as needed instead of permanently employed.
The table below indicates some of the personal information Clean-Q requires as part of its business operations:
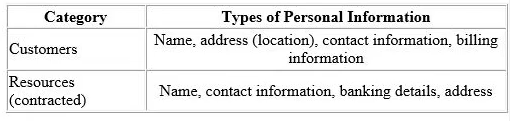
Clean-Q has an internal employee base of about 30 people. A recent privacy compliance exercise has been conducted to align employee data management and human resource functions with applicable data protection regulation. Therefore, the Clean-Q permanent employee base is not included as part of this scenario.
With an increase in construction work and housing developments, Clean-Q has had an influx of requests for cleaning services. The demand has overwhelmed Clean-Q's traditional supply and demand system that has caused some overlapping bookings.
Ina business strategy session held by senior management recently, Clear-Q invited vendors to present potential solutions to their current operational issues. These vendors included Application developers and Cloud-Q's solution providers, presenting their proposed solutions and platforms.
The Managing Director opted to initiate the process to integrate Clean-Q's operations with a cloud solution (LeadOps) that will provide the following solution one single online platform: A web interface that Clean-Q accesses for the purposes of resource and customer management. This would entail uploading resource and customer information.
A customer facing web interface that enables customers to register, manage and submit cleaning service requests online.
A resource facing web interface that enables resources to apply and manage their assigned jobs.
An online payment facility for customers to pay for services.
If Clean-Q were to utilize LeadOps' services, what is a contract clause that may be included in the agreement entered into with LeadOps?
When engaging with a cloud service provider like LeadOps, it's critical to include specific clauses in the contract to ensure the protection and management of personal information. Here's why a notification clause is essential:
Data Breach Notification: A provision requiring LeadOps to notify Clean-Q of any suspected breaches ensures that Clean-Q can take immediate action to mitigate any potential damage, inform affected individuals, and comply with regulatory obligations.
Regulatory Compliance: Many data protection regulations, such as GDPR and CCPA, mandate timely notification of data breaches to both the regulatory authorities and the affected individuals. Including this clause ensures compliance with such laws.
Risk Management: Prompt notification allows Clean-Q to manage and address any risks associated with the breach, including public relations issues and potential legal liabilities.
Transparency and Accountability: This clause promotes transparency and accountability, ensuring that LeadOps maintains a high standard of data security and is responsible for informing Clean-Q about any security incidents.
Which of the following functionalities can meet some of the General Data Protection Regulation's (GDPR's) Data Portability requirements for a social networking app designed for users in the EU?
Allowing users to download the content they have provided to the app meets some of the General Data Protection Regulation (GDPR) Data Portability requirements. GDPR mandates that individuals have the right to obtain and reuse their personal data across different services. By providing a functionality that enables users to download their data, the app facilitates this right, allowing users to easily transfer their information to other services if they choose. This capability directly addresses the data portability requirement specified in Article 20 of the GDPR, ensuring that users maintain control over their personal data. The IAPP documentation on GDPR compliance highlights data portability as a critical aspect of user rights under the regulation.
What must be done to destroy data stored on "write once read many" (WORM) media?
To destroy data stored on 'write once read many' (WORM) media, the media must be physically destroyed. WORM media is designed to prevent data from being modified or erased once written. Therefore, the only effective method to ensure that the data is irretrievable is to physically destroy the media.
IAPP CIPT Study Guide: Data destruction methods for various storage media.
NIST SP 800-88: Guidelines for Media Sanitization, which recommends physical destruction for WORM media.
SCENARIO
You have just been hired by Ancillary.com, a seller of accessories for everything under the sun, including waterproof stickers for pool floats and decorative bands and cases for sunglasses. The company sells cell phone cases, e-cigarette cases, wine spouts, hanging air fresheners for homes and automobiles, book ends, kitchen implements, visors and shields for computer screens, passport holders, gardening tools and lawn ornaments, and catalogs full of health and beauty products. The list seems endless. As the CEO likes to say, Ancillary offers, without doubt, the widest assortment of low-price consumer products from a single company anywhere.
Ancillary's operations are similarly diverse. The company originated with a team of sales consultants selling home and beauty products at small parties in the homes of customers, and this base business is still thriving. However, the company now sells online through retail sites designated for industries and demographics, sites such as ''My Cool Ride" for automobile-related products or ''Zoomer'' for gear aimed toward young adults. The company organization includes a plethora of divisions, units and outrigger operations, as Ancillary has been built along a decentered model rewarding individual initiative and flexibility, while also acquiring key assets. The retail sites seem to all function differently, and you wonder about their compliance with regulations and industry standards. Providing tech support to these sites is also a challenge, partly due to a variety of logins and authentication protocols.
You have been asked to lead three important new projects at Ancillary:
The first is the personal data management and security component of a multi-faceted initiative to unify the company's culture. For this project, you are considering using a series of third- party servers to provide company data and approved applications to employees.
The second project involves providing point of sales technology for the home sales force, allowing them to move beyond paper checks and manual credit card imprinting.
Finally, you are charged with developing privacy protections for a single web store housing all the company's product lines as well as products from affiliates. This new omnibus site will be known, aptly, as ''Under the Sun.'' The Director of Marketing wants the site not only to sell Ancillary's products, but to link to additional products from other retailers through paid advertisements. You need to brief the executive team of security concerns posed by this approach.
If you are asked to advise on privacy concerns regarding paid advertisements, which is the most important aspect to cover?
When dealing with paid advertisements, the most important privacy concern is the collection of personal information by cookies linked to the advertising network.
Cookies and Advertising Networks: Cookies are small data files stored on the user's device by websites to track user behavior and preferences. Advertising networks use these cookies to collect personal information and build detailed user profiles for targeted advertising.
Privacy Concerns: The primary concern is that these cookies can collect a vast amount of personal data without explicit user consent. This data can include browsing habits, location, and sometimes even more sensitive information.
Regulatory Compliance: Various regulations, such as the General Data Protection Regulation (GDPR) in Europe and the California Consumer Privacy Act (CCPA) in the U.S., mandate strict guidelines on how personal data can be collected, stored, and used. Non-compliance can lead to significant legal penalties.
Best Practices: Companies need to ensure transparency about data collection practices, obtain user consent, provide options to opt-out, and implement robust security measures to protect collected data.
IAPP Privacy Management, Information Privacy Technologist Certification Textbooks
GDPR Articles 4, 7, and 21
CCPA Sections 1798.100 - 1798.199
Properly configured databases and well-written website codes are the best protection against what online threat?
SQL injection is a common online threat that targets databases through malicious SQL queries, potentially allowing attackers to access and manipulate database content. Properly configured databases and well-written website code are essential defenses against SQL injection attacks. Ensuring that databases are configured with least privilege access, using parameterized queries, and employing input validation are standard best practices to protect against SQL injection. Pharming (A), malware execution (C), and system modification (D) are different types of threats that require different mitigation strategies. The emphasis on securing databases and writing secure code to prevent SQL injection is well-documented in security guidelines from the Open Web Application Security Project (OWASP) and other cybersecurity frameworks referenced by the IAPP.
- Select Question Types you want
- Set your Desired Pass Percentage
- Allocate Time (Hours : Minutes)
- Create Multiple Practice tests with Limited Questions
- Customer Support
Tiffany Moore
2 months agoRichard Bell
2 months agoElizabeth Wright
3 months agoMelissa Hall
3 months agoCrystal Davis
4 months agoJames Nguyen
4 months agoEmma Lopez
5 months agoMelissa Anderson
5 months agoGerald Harris
6 months agoJustin Martinez
6 months agoJason Wilson
7 months agoNikhil Mishra
2 months agoTimothy Adams
7 months agoNathan Robinson
7 months agoCrystal Williams
6 months agoLinda Campbell
7 months agoPatricia Davis
7 months agoSerina
7 months agoLenna
8 months agoLenna
8 months agoChantell
8 months agoLouvenia
8 months agoGail
9 months agoKenneth
9 months agoKing
9 months agoMonroe
9 months agoValentine
10 months agoBerry
10 months agoNakita
10 months agoStevie
10 months agoReynalda
11 months agoEarleen
11 months agoRashida
11 months agoNettie
11 months agoKayleigh
12 months agoViola
12 months agoGayla
1 year agoQuentin
1 year agoSharen
1 year agoRaul
1 year agoAhmed
1 year agoPearlene
1 year agoCassie
1 year agoKayleigh
1 year agoJeanice
1 year agoLenna
1 year agoCarmelina
1 year agoJennie
1 year agoTomas
1 year agoWillard
1 year agoVerona
2 years agoGlynda
2 years agoTyra
2 years agoDannie
2 years agoJin
2 years agoNoah
2 years agoAdelle
2 years agoTammi
2 years agoJoanna
2 years agoLeatha
2 years agoArmanda
2 years agoStefanie
2 years agoClorinda
2 years agoRoy
2 years agoMatilda
2 years agoHyun
2 years agoHoward
2 years agoMargart
2 years agoAretha
2 years agoKatina
2 years agoLeoma
2 years agoShanice
2 years agoLorenza
2 years agoSena
2 years agoNovella
2 years agoEve
2 years agoRolande
2 years agoLai
2 years agoHubert
2 years agoLorean
2 years agoCatarina
2 years agoFatima
2 years agoGlynda
2 years agoSvetlana
2 years agoShonda
2 years agoDaron
2 years agoBernardo
2 years ago