
Free Preparation Discussions
 MENU

HashiCorp HCVA0-003 Exam Questions
- Topic 1: Authentication Methods: This section of the exam measures the skills of Security Engineers and covers authentication mechanisms in Vault. It focuses on defining authentication methods, distinguishing between human and machine authentication, and selecting the appropriate method based on use cases. Candidates will learn about identities and groups, along with hands-on experience using Vault's API, CLI, and UI for authentication. The section also includes configuring authentication methods through different interfaces to ensure secure access.
- Topic 2: Vault Policies: This section of the exam measures the skills of Cloud Security Architects and covers the role of policies in Vault. Candidates will understand the importance of policies, including defining path-based policies and capabilities that control access. The section explains how to configure and apply policies using Vault’s CLI and UI, ensuring the implementation of secure access controls that align with organizational needs.
- Topic 3: Vault Tokens: This section of the exam measures the skills of IAM Administrators and covers the types and lifecycle of Vault tokens. Candidates will learn to differentiate between service and batch tokens, understand root tokens and their limited use cases, and explore token accessors for tracking authentication sessions. The section also explains token time-to-live settings, orphaned tokens, and how to create tokens based on operational requirements.
- Topic 4: Vault Leases: This section of the exam measures the skills of DevOps Engineers and covers the lease mechanism in Vault. Candidates will understand the purpose of lease IDs, renewal strategies, and how to revoke leases effectively. This section is crucial for managing dynamic secrets efficiently, ensuring that temporary credentials are appropriately handled within secure environments.
- Topic 5: Secrets Engines: This section of the exam measures the skills of Cloud Infrastructure Engineers and covers different types of secret engines in Vault. Candidates will learn to choose an appropriate secrets engine based on the use case, differentiate between static and dynamic secrets, and explore the use of transit secrets for encryption. The section also introduces response wrapping and the importance of short-lived secrets for enhancing security. Hands-on tasks include enabling and accessing secrets engines using the CLI, API, and UI.
- Topic 6: Encryption as a Service: This section of the exam measures the skills of Cryptography Specialists and focuses on Vault’s encryption capabilities. Candidates will learn how to encrypt and decrypt secrets using the transit secrets engine, as well as perform encryption key rotation. These concepts ensure secure data transmission and storage, protecting sensitive information from unauthorized access.
- Topic 7: Vault Architecture Fundamentals: This section of the exam measures the skills of Site Reliability Engineers and provides an overview of Vault's core encryption and security mechanisms. It covers how Vault encrypts data, the sealing and unsealing process, and configuring environment variables for managing Vault deployments efficiently. Understanding these concepts is essential for maintaining a secure Vault environment.
- Topic 8: Vault Deployment Architecture: This section of the exam measures the skills of Platform Engineers and focuses on deployment strategies for Vault. Candidates will learn about self-managed and HashiCorp-managed cluster strategies, the role of storage backends, and the application of Shamir secret sharing in the unsealing process. The section also covers disaster recovery and performance replication strategies to ensure high availability and resilience in Vault deployments.
- Topic 9: Access Management Architecture: This section of the exam measures the skills of Enterprise Security Engineers and introduces key access management components in Vault. Candidates will explore the Vault Agent and its role in automating authentication, secret retrieval, and proxying access. The section also covers the Vault Secrets Operator, which helps manage secrets efficiently in cloud-native environments, ensuring streamlined access management.
Free HashiCorp HCVA0-003 Exam Actual Questions
Note: Premium Questions for HCVA0-003 were last updated On Oct. 20, 2026 (see below)
Jarrad is an AWS engineer and has provisioned a new EC2 instance running MySQL since his application requires a specific MySQL version. He wants to integrate Vault into his workflow but is new to Vault. What secrets engine should Jarrad use to integrate this new database running in AWS?
Comprehensive and Detailed In-Depth
For integrating a MySQL database on an EC2 instance with Vault, the database secrets engine is the appropriate choice:
B . database: 'The 'database' secrets engine in Vault is specifically designed for integrating with databases like MySQL.' It generates dynamic credentials, manages rotations, and supports MySQL plugins, ideal for Jarrad's use case. 'To manage the database resource, the database secrets engine should be used, specifically with the MySQL plugin.'
Incorrect Options:
A . azure: For Azure-specific credential management, not databases. 'Used for generating Azure service principal credentials.'
C . kv: Stores static secrets, not dynamic database credentials. 'Used for storing arbitrary secrets in a key-value pair format.'
D . aws: Manages AWS credentials, not database integration. 'Used for generating AWS access keys.'
The database engine's MySQL support is agnostic to the hosting platform (EC2 vs. RDS), focusing on the database itself.
A developer mistakenly committed code that contained AWS S3 credentials into a public repository. You have been tasked with revoking the AWS S3 credential that was in the code. This credential was created using Vault's AWS secrets engine and the developer received the following output when requesting a credential from Vault.
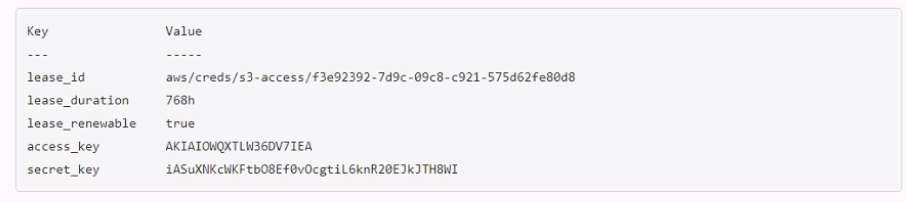
Which Vault command will revoke the lease and remove the credential from AWS?
The correct answer is A because the lease ID is the unique identifier for the credential. The lease ID is used to revoke the credential using the vault lease revoke command. This command will invalidate the credential immediately and prevent any further renewals. It will also delete the access key and secret key from AWS, rendering them useless1. The access key and secret key are not sufficient to revoke the credential, as they are not recognized by Vault. The lease ID is composed of the path of the secrets engine, the role name, and a random UUID. In this case, the path is aws/creds, the role name is s3-access, and the UUID is f3e92392-7d9c-99c8-c921-57Sd62fe89d8.
lease revoke - Command | Vault | HashiCorp Developer
Which of the following is true about the token authentication method in Vault? (Select three)
Comprehensive and Detailed In-Depth
The token auth method is foundational to Vault. The Vault documentation states:
'Tokens are the core method for authentication within Vault. It is also the only auth method that cannot be disabled. If you've gone through the getting started guide, you probably noticed that vault server -dev (or vault operator init for a non-dev server) outputs an initial 'root token.' This is the first method of authentication for Vault. All external authentication mechanisms, such as GitHub, map down to dynamically created tokens.'
--- Vault Concepts: Tokens
A, B, C: Correct per the above.
D: Incorrect; tokens can be used directly:
'Tokens can be used directly or auth methods can be used to dynamically generate tokens based on external identities.'
--- Vault Concepts: Tokens
Vault Concepts: Tokens
When generating a dynamic secret, what value is returned that a user can use to renew or revoke the lease?
Comprehensive and Detailed in Depth Explanatio n:
When Vault generates a dynamic secret, it returns a lease_id, which is the value a user can use to renew or revoke the lease. The HashiCorp Vault documentation states: 'When creating a dynamic secret, Vault always returns a lease_id. This lease_id can be used to do a vault lease renew or a vault lease revoke command to manage the lease of a secret.' The lease_id uniquely identifies the lease associated with the dynamic secret, enabling precise management of its lifecycle.
The documentation under the 'Lease Renew and Revoke' section explains: 'Every secret in Vault is associated with a lease. When that lease expires, Vault revokes the secret and removes access to it. Associated with every lease is a unique lease_id. This identifier can be used to renew the lease before it expires or revoke it manually.' In contrast, renewable is a boolean indicating if the lease can be renewed, not a value for management. token_ttl relates to token duration, not lease management. lease_max is not a standard term in Vault's lease system. Thus, D (lease_id) is the correct answer.
HashiCorp Vault Documentation - Leases: Lease Renew and Revoke
When generating dynamic credentials, Vault also creates associated metadata, including information like time duration, renewability, and more, and links it to the credentials. What is this referred to as?
Comprehensive and Detailed in Depth Explanatio n:
A: Secrets are the credentials themselves, not the metadata. Incorrect.
B: Tokens authenticate clients, not the metadata for credentials. Incorrect.
C: A lease is metadata tied to dynamic secrets, managing their lifecycle (TTL, renewability). Correct.
D: Secrets engines generate secrets, not the metadata. Incorrect.
Overall Explanation from Vault Docs:
''With every dynamic secret... Vault creates a lease: metadata containing TTL, renewability, etc.''
- Select Question Types you want
- Set your Desired Pass Percentage
- Allocate Time (Hours : Minutes)
- Create Multiple Practice tests with Limited Questions
- Customer Support
Dorothy Anderson
1 month agoEric Hernandez
2 months agoMonica Jones
2 months agoLinda Murphy
3 months agoMargaret Martinez
3 months agoWilliam Turner
4 months agoEdward White
4 months agoKevin Allen
5 months agoBrian Torres
5 months agoDeborah Cook
6 months agoDaniel Hernandez
6 months agoJoseph Wilson
6 months agoAmanda Perez
6 months agoCharles Allen
6 months agoChristopher Rogers
6 months agoAmanda Green
6 months agoCecilia
7 months agoSelma
7 months agoMary
7 months agoBilly
8 months agoTimothy
8 months agoDesmond
8 months agoHorace
8 months agoBrinda
9 months agoViola
9 months agoFiliberto
9 months agoJustine
9 months agoYoko
10 months agoNoemi
10 months agoCory
10 months agoJovita
10 months agoErinn
11 months agoFlorinda
11 months agoKathrine
11 months agoBok
11 months agoGlory
12 months agoLynna
12 months agoLawrence
1 year agoDesmond
1 year agoDewitt
1 year agoAileen
1 year agoMarlon
1 year agoShonda
1 year agoFletcher
1 year agoEloisa
1 year agoEdna
1 year agoAmos
1 year agoDominga
1 year agoEliz
1 year agoCorinne
1 year agoAlaine
1 year agoMalcolm
1 year agoAnnice
1 year agoHubert
1 year agoLizbeth
2 years agoAmie
2 years agoRolland
2 years agoKristeen
2 years agoDella
2 years ago